How to Give Users TestLight Access by Defining Custom Roles and Permission Sets
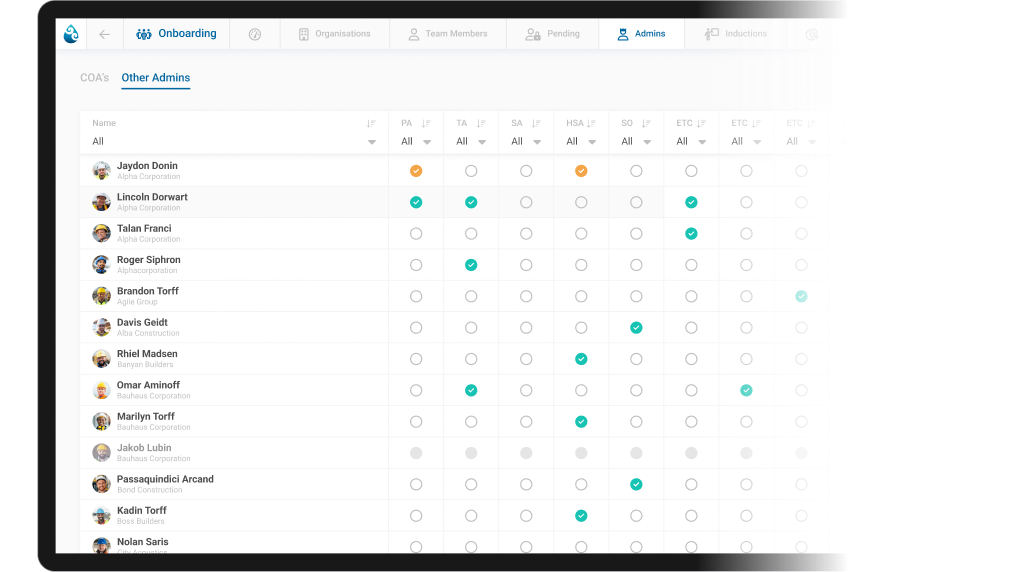
Table of Contents
- Understanding TestLight Access Requirements and User Roles
- User Roles and Permissions, How to give users testlight access
- Default User Roles in TestLight
- Designing an Effective User Access Management Strategy: How To Give Users Testlight Access
- Creating a Custom User Role with Tailored Permission Settings
- User Role Hierarchy within TestLight
- Security Best Practices for Enforcing Least Privilege Access
- Best Practices for Maintaining TestLight User Access Levels
- User Role Clean-up and Permission Set Optimization
- Automating TestLight User Access Management
- Ending Remarks
- Question & Answer Hub
How to give users TestLight access is a crucial step in ensuring that your team members have the appropriate level of access to perform their tasks efficiently without compromising the security of your TestLight system. Understanding the various user roles and permissions in TestLight is essential to provide context for access management.
The various user roles in TestLight, including Administrators, Moderators, and Contributors, each have specific privileges and are designed to maintain system integrity. It's essential to create a custom user role with tailored permission settings to ensure that users have the necessary access to perform their tasks without over-privileging them.
Understanding TestLight Access Requirements and User Roles
In the realm of TestLight, a delicate balance is maintained by the subtle dance of user roles and privileges. Each participant, whether a developer, tester, or administrator, is assigned a unique role that governs their interaction with the system. This nuanced hierarchy is crucial in ensuring the integrity and security of TestLight.
User Roles and Permissions, How to give users testlight access
The foundation of TestLight's access management lies in its user roles. These roles define the scope of permissions, duties, and privileges associated with each user. Understanding the various user roles and their corresponding permissions is essential for effective access management.
"User roles are the threads that weave the fabric of TestLight's access management system."
Default User Roles in TestLight
TestLight employs a set of default user roles, each with its unique set of privileges. These roles serve as a foundation for custom roles, allowing administrators to fine-tune access management tailored to their organization's specific needs.
| Role | Description | Privileges |
| --- | --- | --- |
| Admin | System Administrator | Full control, including role management and security settings |
| Dev | Developer | Ability to create, modify, and deploy tests |
| QA | Quality Assurance | Permission to run, analyze, and report test results |
| Viewer | User with limited access | Ability to view test results and reports |
### Importance of User Role Granularity
TestLight's user management system boasts a high degree of granularity, enabling administrators to create custom roles with tailored permissions. This flexibility is crucial in maintaining the system's integrity by preventing excessive privileges and ensuring that access is restricted to authorized users only.
"A well-defined user role hierarchy is the cornerstone of TestLight's access management strategy."Each custom role can be designed with specific permissions, duties, and privileges to suit the organization's unique needs. This level of control enables administrators to fine-tune access management and ensure that users have the exact level of access required to perform their tasks efficiently.
Designing an Effective User Access Management Strategy: How To Give Users Testlight Access
In the realm of TestLight, where permissions and roles converge, a well-crafted user access management strategy is a symphony of precision and control. A delicate balance between user empowerment and system security is a tale of contrasts, where too little access yields frustration, while too much exposes vulnerabilities.Creating a Custom User Role with Tailored Permission Settings
A bespoke user role, crafted to suit the needs of your organization, is a masterpiece of flexibility and functionality. To create such a role, follow these steps, each a brushstroke on the canvas of access control.* Identify the functions and features that require permissions
User Role Hierarchy within TestLight
A well-structured user role hierarchy is a pyramid of privilege and responsibility. Below, a table illustrates the roles, their descriptions, and the associated permissions.| User Role | Description | Permissions | Example Users |
|---|---|---|---|
| Admin | Total control over TestLight, with unlimited access to all features and permissions. | All permissions | Only a select few, with full responsibility for system management. |
| Manager | Full control over user roles and permissions, with limited access to sensitive features. | Manage user roles and permissions, access to sensitive features with approval | Department heads and team leads. |
| Editor | Limited access to content editing and management, with some permissions for publishing. | Manage content, publish updates with approval | Content creators and writers. |
| Viewer | Restricted access to content viewing, with no permissions for editing or publishing. | View content | End-users and consumers of content. |
Security Best Practices for Enforcing Least Privilege Access
In the realm of security, least privilege access is the golden rule. Granting users only the permissions they need to perform their duties ensures that vulnerabilities are minimized and risks are mitigated.* Implement role-based access control (RBAC) to ensure that users are assigned to roles based on their job functions.
Best Practices for Maintaining TestLight User Access Levels

Monitoring TestLight user access levels is crucial to prevent unauthorized activity. Think of it as patrolling a vast digital landscape, ever vigilant for signs of mischief or unauthorized access. This can be achieved by:
- Regularly reviewing user access logs to identify suspicious activity.
- Implementing automated alerts for unauthorized access attempts.
- Conducting regular security audits to ensure compliance with organizational policies.
To maintain a healthy and efficient user access ecosystem, it's vital to conduct regular user role clean-up and permission set optimization in TestLight. This is akin to pruning a garden, removing dead branches and allowing new growth to flourish.
User Role Clean-up and Permission Set Optimization
When user roles and permission sets become cumbersome, it's time to revisit and refine them. This process can be broken down into several steps:- Identify orphaned user roles and retire them.
- Streamline permission sets by removing redundant or unnecessary permissions.
- Migrate users to more suitable roles and permission sets.
- Regularly review and update user roles and permission sets to ensure they remain relevant.
Designing an example workflow for automating TestLight user access management tasks is a vital step in maintaining a harmonious and secure environment. Like a maestro conducting an orchestra, you'll be able to orchestrate user access with ease and precision.
Automating TestLight User Access Management
Imagine a workflow that could automate user access management, freeing you from tedious manual tasks and allowing you to focus on higher-level strategy. This workflow could include:- Creating a centralized repository for user access requests.
- Implementing automated user access workflows for common tasks.
- Integrating with other systems to synchronize user access information.
- Maintaining a comprehensive audit trail of all user access changes.
Ending Remarks
In conclusion, giving users TestLight access requires a thoughtful and strategic approach that takes into account the various user roles and permissions available in the system. By defining custom roles and permission sets, you can ensure that your team members have the necessary access to perform their tasks efficiently while maintaining the security of your TestLight system.
Question & Answer Hub
Q: What is the difference between permission sets and role-based access control in TestLight?
A: Permission sets in TestLight refer to a collection of specific permissions that define a user's level of access to a resource. Role-based access control, on the other hand, is a system where a user is assigned to a specific role that defines their level of access to resources.
Q: How do I grant a user access to multiple permission sets in TestLight?
A: To grant a user access to multiple permission sets in TestLight, you need to assign the user to a specific role that has been configured to include the relevant permission sets. You can do this by navigating to the user's profile and assigning the role to the user.
Q: What is the significance of regular user role audits to ensure ongoing TestLight system security?
A: Regular user role audits are essential to ensure that users' access levels are up-to-date and aligned with their job responsibilities. This helps prevent over-privileging and ensures that the TestLight system is secure.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of guessthescore.