How to View all the Github Protected Branches at a Glance

Table of Contents
- Understanding GitHub Protected Branches in Modern Development Environments: How To View All The Github Protected Branches
- Different Types of Protected Branches
- Applications of Protected Branches
- Use Cases for Protected Branches
- Real-World Examples
- Accessing and Listing Protected Branches on GitHub using CLI and API
- Authenticating with a Personal Access Token
- Listing Protected Branches using the GitHub CLI
- Filtering Protected Branches using API Parameters
- Using API Parameters for Filtering
- Viewing Protected Branch Permissions and Access Control
- Different Levels of Access Control Available for Protected Branches
- Admin
- Write
- Read
- Maintain
- Scenarios Where Fine-Grained Access Control is Essential
- Best Practices for Configuring Access Control
- Managing and Updating Protected Branch Settings using GitHub UI
- Navigating to the Branch Settings Page on GitHub
- Changing and Customizing Branch Permissions Settings, How to view all the github protected branches
- Benefits and Drawbacks of Updating Branch Settings Using the Web Interface
- Conclusive Thoughts
- Answers to Common Questions
As how to view all the github protected branches takes center stage, this opening passage invites readers into a realm of profound understanding, where the intricate web of protected branches is laid bare. By delving into the world of modern development environments, we will reveal the significance of protected branches in safeguarding sensitive project code, different types of protected branches, and their applications.
Moreover, we will explore the steps to authenticate with GitHub using a personal access token, the syntax for listing protected branches using the GitHub CLI, and how to filter protected branches using API parameters.
Understanding GitHub Protected Branches in Modern Development Environments: How To View All The Github Protected Branches
In modern development environments, controlling changes to sensitive project code is a crucial aspect of maintaining the stability and security of a project. This can be achieved through the use of protected branches in GitHub, which provide a layer of protection against unauthorized changes or pushes to sensitive branches.
GitHub protected branches allow administrators to control and enforce certain rules and permissions for specific branches in a repository. This includes specifying which users or teams can push to a protected branch, as well as any additional validation steps that must be taken before changes can be made.
Different Types of Protected Branches
There are two primary types of protected branches in GitHub: release branches and feature branches.Release branches are used for the final stages of testing before a new release is made. These branches are typically protected to ensure that only authorized users can push changes to them, and that any changes made must pass certain validation checks. This helps to prevent bugs and regressions from being introduced into the release, and ensures that the final version of the code is stable and reliable.
Feature branches, on the other hand, are used for new features or changes that are still in development. These branches are also protected to ensure that only authorized users can push changes to them, and that any changes made must follow a set of established rules and guidelines.
Applications of Protected Branches
Protected branches have a wide range of applications in modern development environments, including:- Ensuring code quality and stability: By enforcing specific rules and permissions for protected branches, developers can ensure that code is reviewed and tested thoroughly before it is released. This helps to prevent bugs and regressions from entering the codebase.
- Managing access and permissions: Protected branches allow administrators to control and manage access to sensitive branches, ensuring that only authorized users can make changes.
- Streamlining workflows: By automating certain tasks and validation steps for protected branches, developers can streamline their workflows and increase productivity.
- Improving security: Protected branches help to prevent unauthorized changes or pushes to sensitive branches, reducing the risk of security vulnerabilities and data breaches.
Use Cases for Protected Branches
Protected branches offer a layer of code security in a variety of use cases, including:- Maintaining a stable production branch: Protected production branches ensure that only authorized users can push changes to them, and that any changes made must follow established rules and guidelines.
- Developing new features or changes: Protected feature branches ensure that only authorized users can make changes, and that any changes made must follow established rules and guidelines.
- Testing and validation: Protected branches can be used to enforce specific rules and permissions for testing and validation, ensuring that code is reviewed and tested thoroughly before it is released.
Real-World Examples
The use of protected branches can be seen in a variety of real-world examples, including:- Apple Inc: Apple uses GitHub protected branches to control changes to sensitive branches, ensuring that only authorized users can make changes and that any changes made must follow established rules and guidelines.
- Microsoft: Microsoft uses GitHub protected branches to manage access and permissions to sensitive branches, ensuring that only authorized users can make changes.
Accessing and Listing Protected Branches on GitHub using CLI and API
To access and list protected branches on GitHub using the Command Line Interface (CLI) and API, developers need to be familiar with GitHub's authentication methods and the syntax for listing protected branches.One of the essential steps in using GitHub's CLI or API is authenticating with a personal access token. Authenticating with a personal access token provides an additional layer of security and flexibility compared to using a username and password.
Authenticating with a Personal Access Token
To authenticate with a personal access token, follow these steps:- Generate a personal access token on your GitHub account page. Go to Settings > Developer settings > Personal access tokens.
- Copy the generated token and store it securely. You will need to use this token to authenticate with the GitHub CLI or API.
- Configure the GitHub CLI or API to use your personal access token. The syntax for this step will be discussed in the next section.
Listing Protected Branches using the GitHub CLI
Once authenticated, you can use the GitHub CLI to list protected branches. The following syntax is used:gh api /repos/owner/repo/branches | jq '.[0].name'This syntax lists the names of the protected branches for a specific repository. Replace owner with the name of the repository owner and repo with the name of the repository.
gh api /repos/owner/repo/branches --jq '.[] | select(.protected) | .name'This syntax lists only the names of the protected branches for a specific repository, excluding non-protected branches.
Filtering Protected Branches using API Parameters
The GitHub API provides various parameters for filtering protected branches. The following parameters can be used:- state: This parameter can be used to filter protected branches based on their state (e.g., enabled or disabled).
- pattern: This parameter can be used to search for protected branches that match a specific pattern.
- include_ref_in_diff_url: This parameter specifies whether the ref should be included in the difference URL.
GET /repos/owner/repo/branches?state=enabled&pattern=mainThis API call lists all protected branches in the specified repository that match the pattern main and have the state set to enabled.
Using API Parameters for Filtering
To use API parameters for filtering protected branches, you need to include the parameter in the API call. The following API call lists protected branches that match a specific pattern and have the state set to enabled:GET /repos/owner/repo/branches?state=enabled&pattern=main&include_ref_in_diff_url=trueThis API call lists all protected branches in the specified repository that match the pattern main, have the state set to enabled, and include the ref in the difference URL.
Viewing Protected Branch Permissions and Access Control
Branch permissions allow you to assign different levels of access to various team members, ensuring that only authorized individuals can push code to protected branches. This helps maintain the quality and stability of your codebase, as well as ensures that changes are made in a controlled and regulated manner.
Different Levels of Access Control Available for Protected Branches
There are several levels of access control available for protected branches on GitHub, each offering varying degrees of granular control. These include:Admin
A user with admin access can push, pull, merge, or delete the protected branch, making them the ultimate authority on the branch. Admins can also manage permissions and add or remove team members from the branch.Write
A user with write access can push to the protected branch, but cannot delete it or manage permissions. This level of access control allows team members to contribute to the branch without compromising its integrity.Read
A user with read access can only pull from the protected branch, making them able to view the codebase without being able to modify it. This level of access control is suitable for team members who need to review or audit the code.Maintain
A user with maintain access can merge and push to the protected branch, but cannot delete it or manage permissions. This level of access control is suitable for team members who need to resolve conflicts or update the branch.
Scenarios Where Fine-Grained Access Control is Essential
Fine-grained access control is crucial in certain scenarios where maintaining branch integrity is of utmost importance. Some examples include:Feature Branches
When developing feature branches, you need to ensure that only authorized team members can push changes to the branch. Fine-grained access control allows you to assign specific permissions, preventing accidental or malicious changes.Long-Term Maintenance Branches
When maintaining long-term branches, you need to ensure that only trusted team members can push changes to the branch. Fine-grained access control allows you to assign specific permissions, preventing unexpected changes from negatively impacting the codebase.Production Branches
When maintaining production branches, you need to ensure that only authorized team members can push changes to the branch. Fine-grained access control allows you to assign specific permissions, preventing unexpected changes from negatively impacting the production environment.
Best Practices for Configuring Access Control
When configuring access control for protected branches, it's essential to follow best practices to ensure seamless collaboration and maintain branch integrity:Assign Specific Permissions
Instead of assigning general permissions, assign specific permissions to team members, ensuring that each user has only the necessary access to the branch.Monitor and Review Logs
Regularly monitor and review branch logs to track changes and detect potential security breaches.Configure Webhooks
Configure webhooks to send notifications when changes are made to the protected branch, ensuring that team members are informed of any updates.
Managing and Updating Protected Branch Settings using GitHub UI
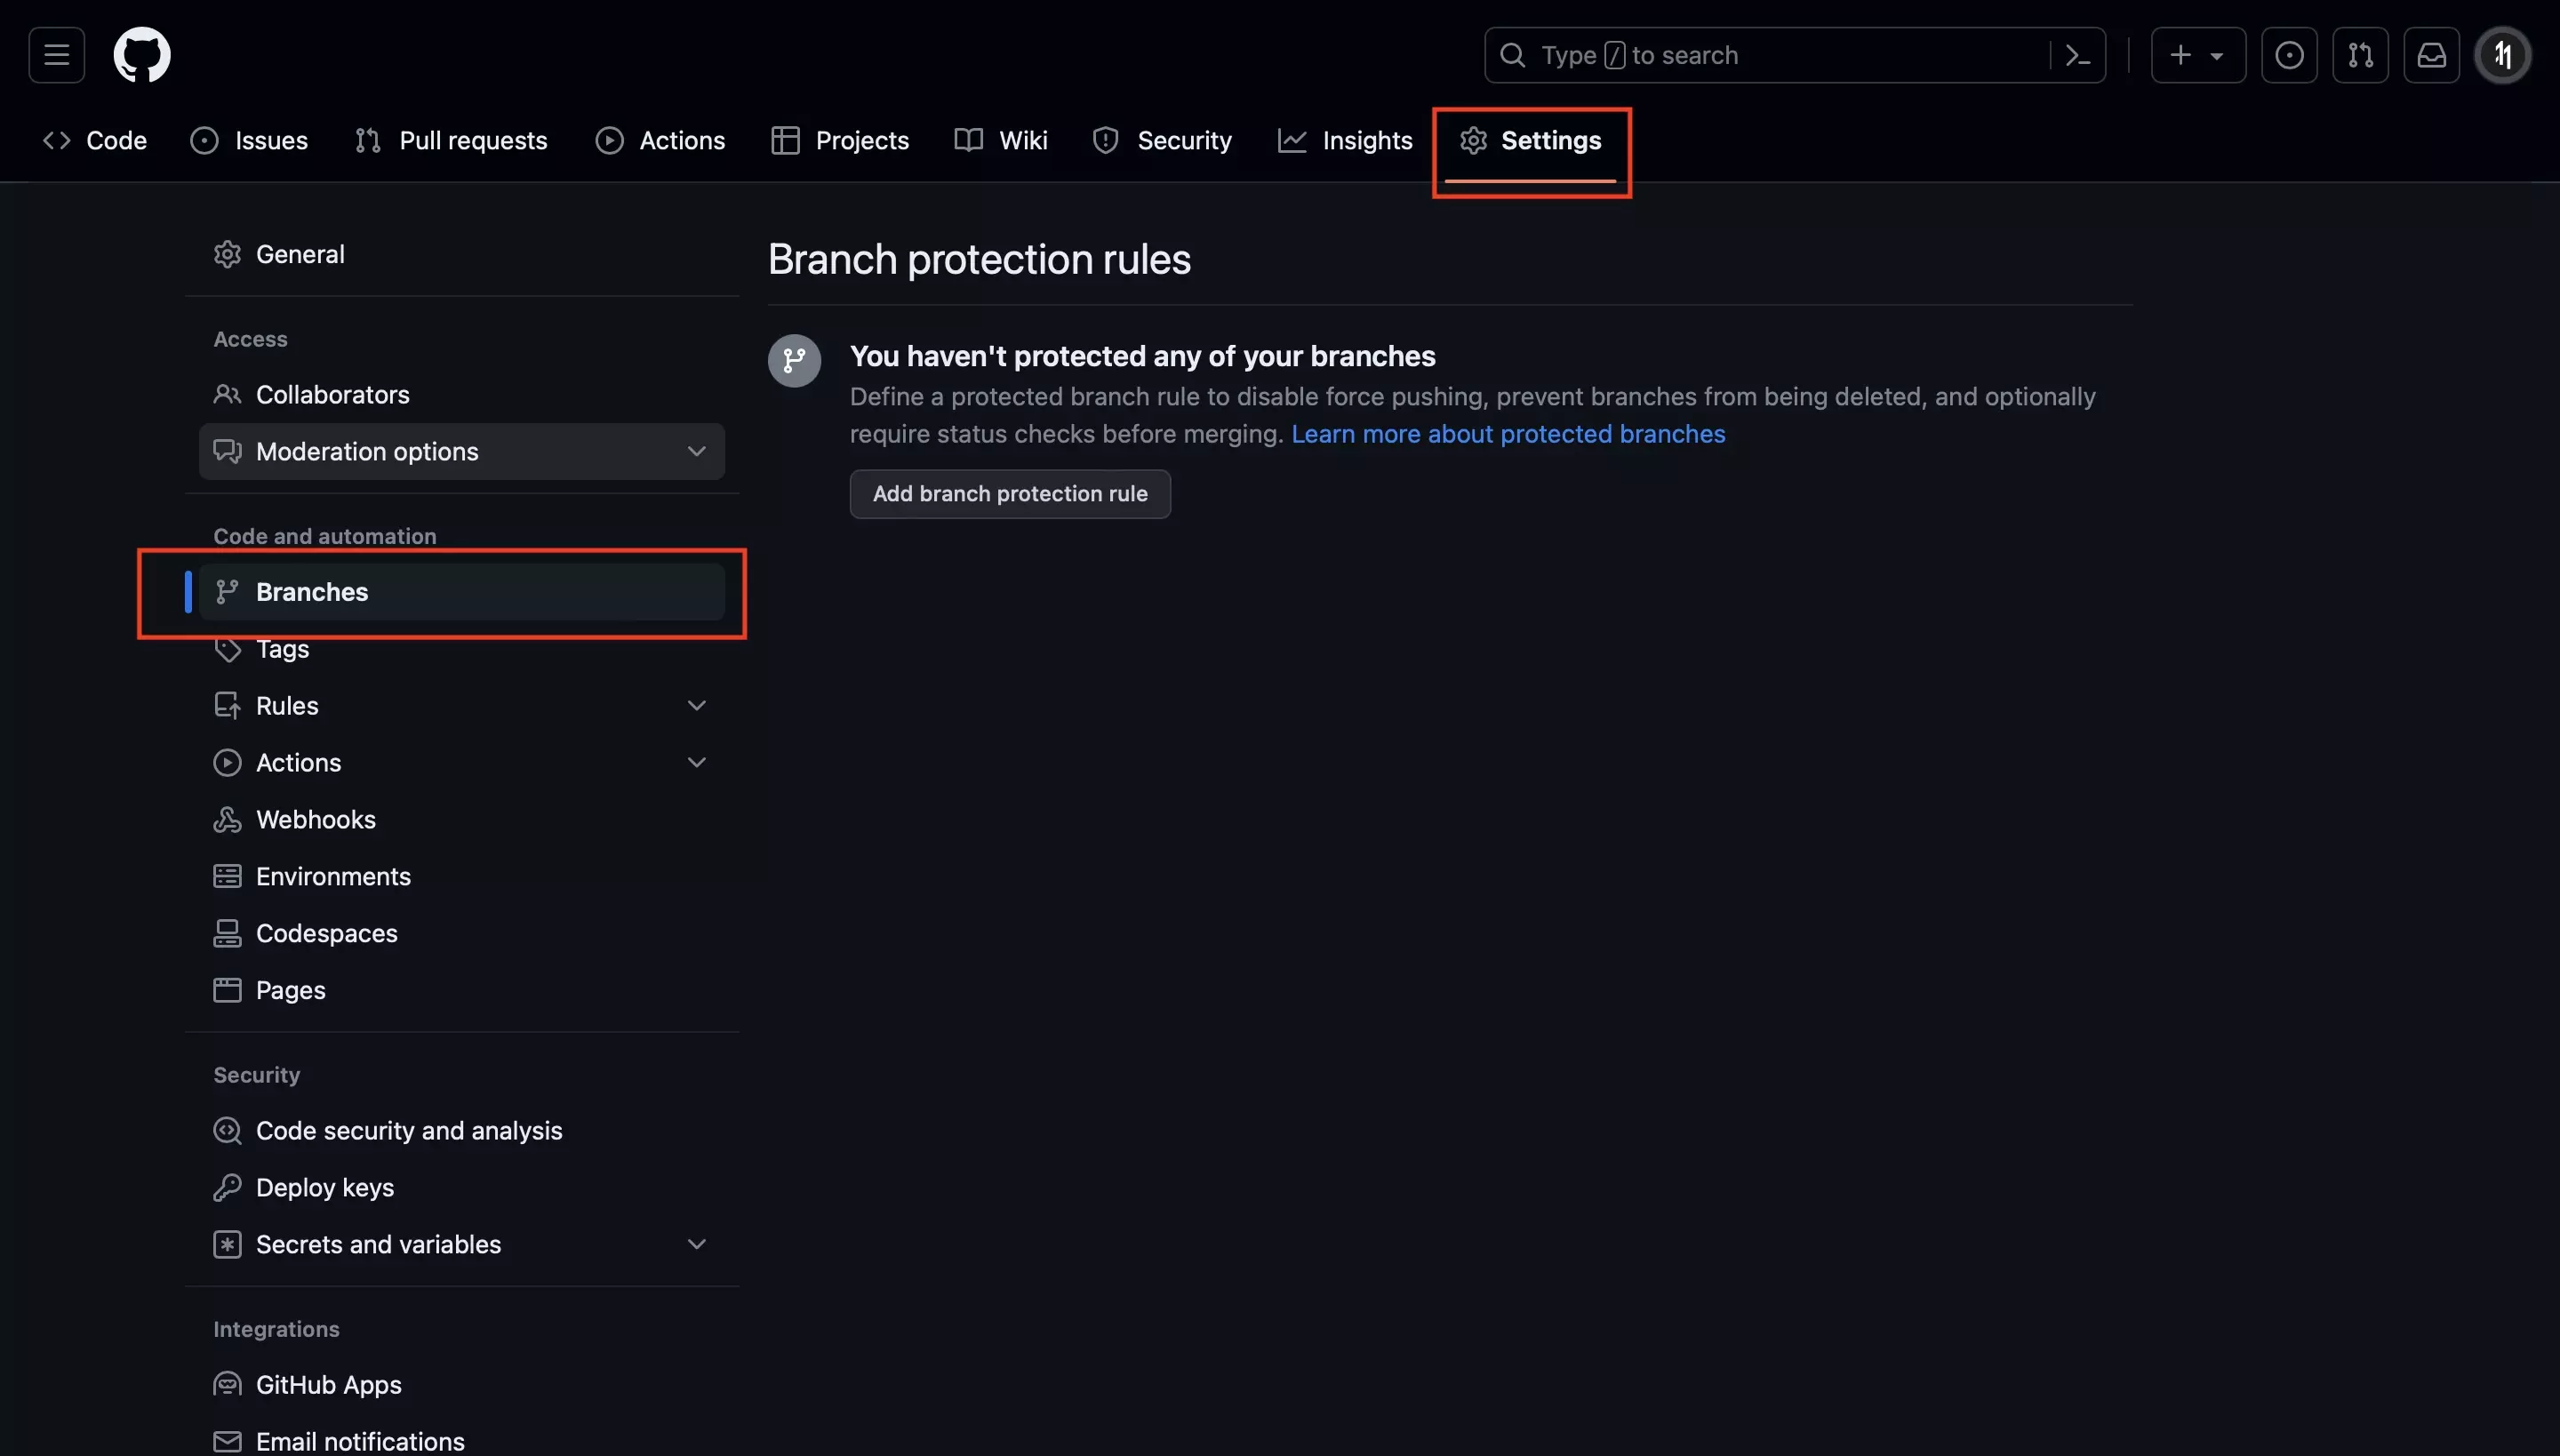
Navigating to the Branch Settings Page on GitHub
To manage protected branch settings using the GitHub UI, follow these steps:1. Log in to your GitHub account and navigate to your repository.
2. Click on the repository's name to access its dashboard.
3. In the left-hand menu, select the branch you wish to manage.
4. Click on the three dots at the top right corner of the branch name and select "Branch settings".
Changing and Customizing Branch Permissions Settings, How to view all the github protected branches
Once you're on the branch settings page, you can modify the permissions settings. The following permissions can be customized:- Push permissions
- Merge permissions
- Allow force pushes
- Allow deletions
Benefits and Drawbacks of Updating Branch Settings Using the Web Interface
The web interface provides a user-friendly way to manage protected branch settings. It allows for easy customization of permissions and provides real-time feedback. However, it may not offer the same level of automation as the GitHub API.By updating branch settings using the web interface, you can:
- Quickly modify permissions settings
- Easily visualize the changes
- Access a user-friendly interface
Conclusive Thoughts
With this in-depth exploration, readers will gain a comprehensive understanding of how to view all the github protected branches, enabling them to navigate the complex landscape of branch permissions, access control, and integration with CI/CD pipelines. By mastering the art of protected branches, developers can safeguard their project code, ensuring the long-term sustainability of their projects.
Answers to Common Questions
What are the different types of protected branches on GitHub?
There are two types of protected branches on GitHub: required status checks and required approvals. Required status checks ensure that certain checks, such as code lints, are satisfied before a branch can be merged, while required approvals restrict the ability to push code to a branch.
Can I use a personal access token to list protected branches using the GitHub CLI?
Yes, you can use a personal access token to authenticate with GitHub and list protected branches using the GitHub CLI. However, make sure to use a token with the appropriate scopes to avoid any errors.
What are the benefits of integrating protected branches with CI/CD pipelines?
By integrating protected branches with CI/CD pipelines, developers can automate the process of branch protection, ensuring that only valid code makes it to production. This streamlines the development process, reduces errors, and enhances the overall quality of the software.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of guessthescore.